

1. The Critical Need for Passkey Intelligence
Passkey Intelligence drives the passkey flywheel across all industries: more passkeys created, more logins with passkeys and fewer errors.
The flywheel leads to higher user retention, more successful logins and lower support costs, whatever your product category.
Without an intelligence layer, users quickly run into confusing dead ends. Real-world data shows why:
- High device turnover: About 15% of users try to sign in from a different device than the one holding their passkey within 3 months of account creation. Within 6 months, it is 35%.
- Failing OS dialogs: On the web, the frontend cannot know whether a passkey is accessible on the current device. Native prompts can open and then find no credential, which leaves users stuck.
- QR code loops: If no passkey is found locally, most browsers assume it is on a phone and show a QR code for cross-device login. Without guidance, users abandon the flow.
- Third-party password managers: 5–10% of passkeys are stored in non-platform managers such as 1Password, Dashlane or Bitwarden. These are not available on every OS and browser combination, so a passkey that worked on one device or browser may be inaccessible on another.
- Mobile fragmentation: Alongside first-party managers such as iCloud Keychain and Google Password Manager, many third-party password managers integrate deeply into the OS. Android adds manufacturer implementations such as Samsung Pass and several variants of the Credential Manager API. Native passkey interfaces also change quickly, which makes a consistent experience hard without an intelligence layer.
- Missing managers on new devices: About 50% of users who first used a password manager do not have it installed on their next device. This breaks cross-device journeys.
- Raw failure rate: 5–10% of all WebAuthn operations fail or time out when attempted blindly. They often end with an unexplained QR code or security-key prompt.
2. How Passkey Intelligence Works
Passkey Intelligence is the decision layer of Corbado Connect. It starts a passkey login or creation ceremony only when success is likely and falls back gracefully when it is not. It powers One-Tap login, cross-device sign-in and context-aware prompts.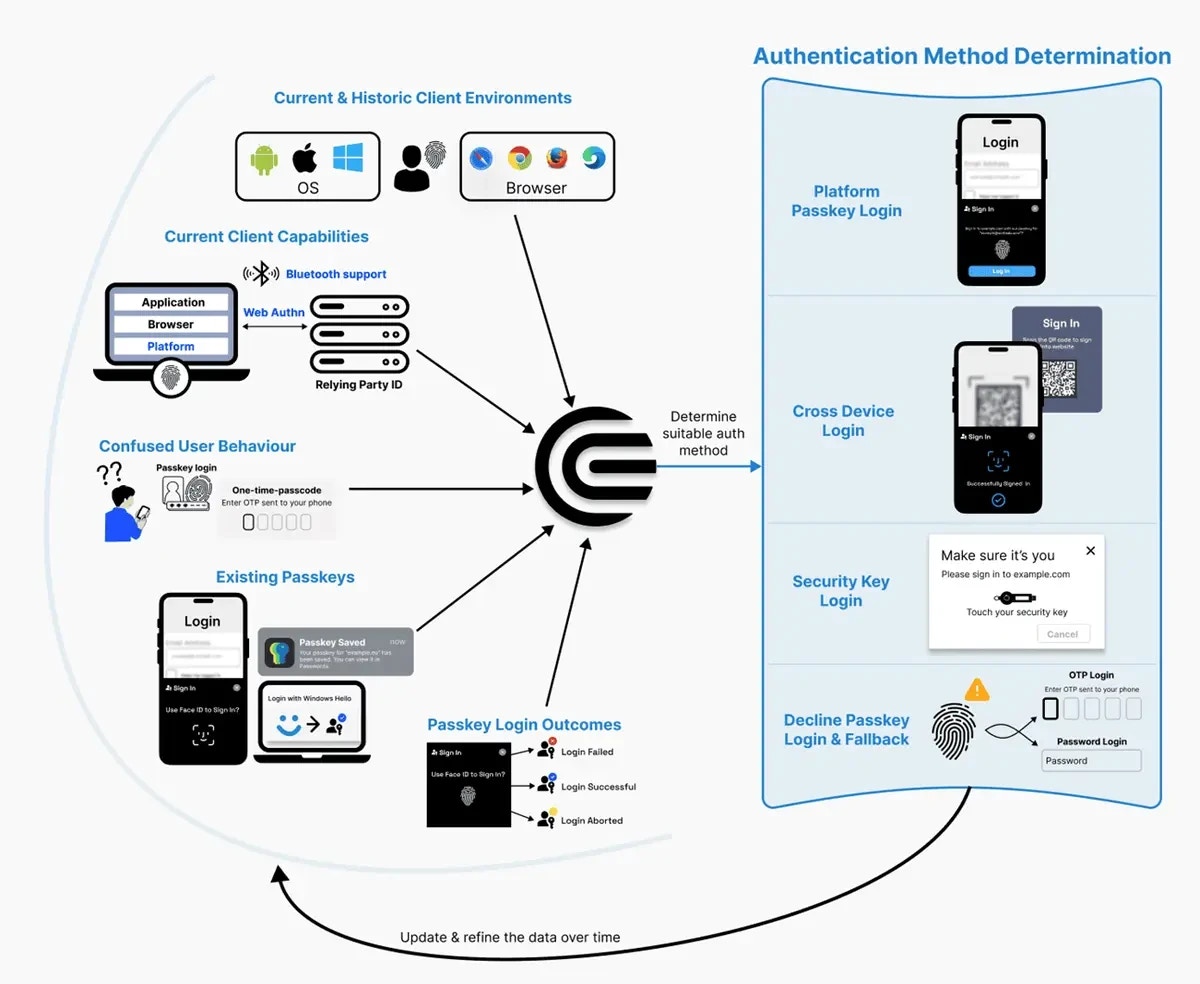
- Device and browser capabilities: Operating system, browser version and WebAuthn support. Hardware features such as biometric sensors or Bluetooth show whether passkeys and cross-device options work. In native iOS and Android apps, the engine also checks screen lock availability and the status of cloud accounts such as iCloud Keychain and Google Password Manager.
- Passkey history: Whether the user has created or used a passkey before and on which devices. Successful passkey logins and fallbacks to passwords or OTP inform future decisions. Synced passkeys in a cloud account or password manager are noted for cross-device availability.
- Interaction behavior: How users react to passkey prompts, for example cancellations, errors, skipped offers and switches to other methods. This decides when to prompt them again.
- Error analysis: All error messages from the WebAuthn APIs on web, iOS and Android are recorded and classified. Corbado uses them to improve the decision logic, fix bugs and adapt to changes by platform vendors and third-party passkey providers such as 1Password and Dashlane.
- Security and risk signals: Unusual login patterns, IP or location changes and device integrity signals. If something looks suspicious or the environment is not passkey-ready, the engine avoids the passkey prompt and chooses a safer fallback.
- Local device flags: After a successful passkey login, a small flag in the browser, for example in
localStorage, records that this user has a passkey on this device. On the next visit, the UI can offer One-Tap login directly without additional server checks. - Enrollment situation: The web and native SDKs pass the context of an enrollment offer, for example after login or at another authenticated point in your app. Rules can treat these contexts differently.
- Automatic passkey login: Starts the platform passkey ceremony directly.
- One-Tap button: Shows a passkey login button prefilled with the user’s identifier.
- Cross-device login: Offers a QR code when no local credential is available.
- Fallback: Continues with your password or OTP flow.
3. Key Benefits of Passkey Intelligence
The diagram shows how Passkey Intelligence decides between a passkey ceremony and your existing authentication. It follows two principles: maximize successful passkey logins (green path) and minimize failed or confusing experiences (red path). On the green path, users log in with a quick biometric check. On the red path, they continue with the familiar password or 2FA flow and never reach a dead end.- Seamless UX and higher success rates: The passkey prompt appears only when the user can likely complete it. Users see far fewer errors and failed logins. Avoiding dead ends, such as passkey prompts on unsupported devices, builds trust in the new login method.
- Maximized passkey adoption: Passkey Intelligence raises the passkey login rate, the share of all logins completed with passkeys instead of passwords or OTP. High passkey usage means fewer password resets and lower MFA costs for SMS and OTP, with security and ROI benefits.
- Smooth fallbacks without dead ends: If a passkey is unavailable or unlikely to work, for example on a work PC without the user’s personal passkey, the flow switches to the next-best method before the user notices. Users see no confusing error messages or unnecessary QR codes. The same signals, such as cancelled prompts or inactive first-party cloud accounts, show whether a user is ready for a passwordless-only experience. This prevents premature passkey enforcement.
- Cross-device convenience: Passkey Intelligence uses cloud-synced passkeys and multi-device credentials. If the passkey is on another device, the user gets clear guidance through the QR code login and is then offered a new local passkey. For example, a user’s only passkey is on their phone. They scan the QR code on their laptop, confirm on the phone and are logged in. The laptop then offers a local passkey, so the next login needs no QR code.
- Adaptive to user behavior: The engine learns from your user base. Patterns such as many users aborting at one step or skipping passkey prompts lead to adjusted flows. Error messages from the native iOS and Android SDKs also improve the web experience, so insights from one platform benefit all users. All error messages are classified continuously to handle new edge cases.
- Enterprise-grade security controls: Every login attempt is evaluated for risk. Suspicious signals, such as repeated rapid failures or a new device in a distant location, make the engine more conservative. It may skip the automatic passkey prompt and require an extra verification step.
clientStatemanagement: After a successful passkey operation, Corbado returns aclientStatestring with encoded environment information such as device capabilities and passkey availability. The SDK keeps it in the browser’slocalStorage. Passing it back into the Corbado Web UI Components speeds up loading and enables flows like One-Tap login without repeated environment checks. See how to manageclientState.
4. One-Tap Login
One-Tap Login is one of the flagship features of Passkey Intelligence. Returning users authenticate with a single tap plus a biometric check, without entering their identifier again. The dynamic One-Tap Passkey Button appears for users who have used a passkey on this device before. It makes login simple, fast and secure, which also boosts passkey adoption. Include account switching and shared devices in your design. See One-Tap Login for how it works and its benefits.5. Integration in Login and Signup Flows
Passkey Intelligence supports identifier-first (automatic) flows and explicit passkey button flows. Compare both in login approaches.5.1 Identifier-First Login Flows
The user first enters an identifier, such as an email address, username or customer number. The engine then decides whether to start a passkey login right away. If yes, the WebAuthn ceremony starts automatically. If not, the flow silently continues with your next step, for example a password or OTP. Users log in with a passkey whenever possible and are never confused by a failed attempt. Your web callbacks or native SDK state handlers continue the fallback journey.5.2 Separate Passkey Button Flows
Many applications show a “Login with passkey” button next to the traditional login form. Users can start without entering an identifier. Passkey Intelligence adds the One-Tap Passkey Button: at first you display a normal “Use passkey” button. Once a user becomes eligible, the component switches to One-Tap mode on later visits and shows a personalized prompt such as “Login with passkey for alice@example.com”.5.3 Signup and Registration Flows
Passkey Intelligence also increases passkey enrollment. When a new user signs up or an existing user logs in with a password, Corbado can prompt them to create a passkey. Your identity system completes sign-up and authentication first. You configure how this happens. Some services start passkey creation automatically after a standard login on a supported device. Others show an explanation screen first. Corbado’s components offer customizable enrollment screens that you can enable or skip and tailor by device type. Offer enrollment after fallback logins too, because an existing passkey may not be available on this device.6. Passkey Creation and Autofill
Passkey Intelligence optimizes the whole journey from creating a passkey to using it.6.1 Passkey Creation
If a user on a passkey-capable device logs in with another method, such as a password, the engine can guide them straight to passkey creation:- Automatic passkey creation: The ceremony starts without an extra click, often right after the first login.
- Passkey explainer screens: For an explicit opt-in, disable automatic creation and use the Append Passkey Prompt. This modal or page explains the benefits after sign-up or login and asks the user to continue.
- Conditional creation: An eligible password-autofill login is upgraded to a passkey without the usual creation prompt. Platform prerequisites and SDK support differ. The native enrollment guide describes the current iOS and Android behavior, including the Android SDK limitation. To try it on the web, open the demo and let a password manager that supports it fill in your password.
create() call then runs, and the device stores the new passkey in its platform authenticator or password manager.
6.2 Autofill and One-Tap Behavior
Using a passkey after creation should be effortless. Modern browsers support Conditional UI, a built-in autofill for passkeys. With the right setup, the browser shows a prompt such as “Use your passkey for example.com” or an account chooser as soon as the login form appears. Passkey Intelligence works hand in hand with Conditional UI. Where it is unsupported or ignored, the One-Tap Passkey Button keeps a one-tap option visible for returning users. The engine prefills the button with the identifier from the last passkey login. It works like “Remember me” for passkeys: the user types no email address, and the button shows the account that signs in with a biometric check.7. Additional Resources
- Passkey Intelligence, login identifiers and verification: This article introduces Passkey Intelligence and related features such as login identifiers and custom flows.
- High passkey adoption in login flows: This guide covers data and case studies on passkey login rates, One-Tap Passkey Buttons and intelligence-driven strategies.
- Web integration: Login callbacks and enrollment callbacks.
- Native integration: Enrollment, login and management.
- Rollout validation: Verify and roll out.